Base44 logoVibe-coding platform·Base44

Base44 + Powabase

Base44 assembles the tool. Powabase is the part that has to hold up.

Base44 builds a whole app from a prompt with no setup. Connect a Powabase project and those apps run on real Postgres with real sign-in and proper access control, instead of throwaway storage.

Rather have it built? Powabase engineers build MVPs free for annual Scale and Enterprise plans.

Quick start

Three steps and Base44 is building on Powabase.

  1. 1

    Create a Powabase project

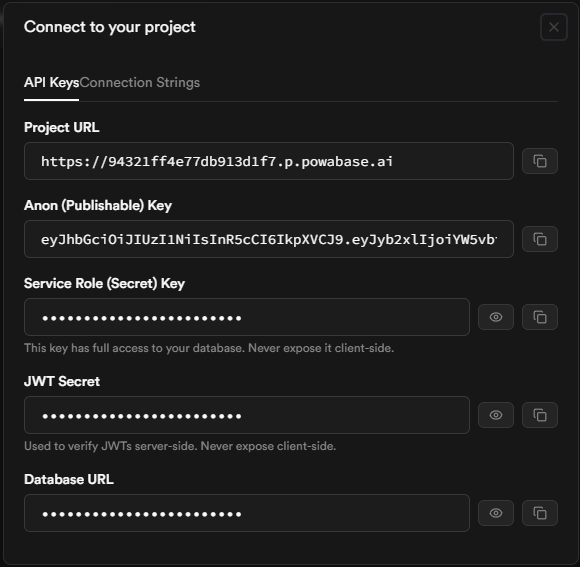
    Create a project at app.powabase.ai and open the Connect dialog (top-left in Studio). Copy the Project URL and the Service Role (Secret) Key. The Service Role key reaches everything: the agent and AI endpoints, plus full database access. Keep it on the server and never put it in the browser.

    The Powabase Connect dialog showing the Project URL, Anon key, Service Role key, JWT secret, and Database URL
    The Connect dialog in Powabase Studio.
  2. 2

    Connect the API

    Add the Project URL and Service Role key as a server-side integration. Don't expose the Service Role key in anything that runs in the browser.

    Integration
    BASE_URL=<Project URL>
    API_KEY=<Service Role (Secret) Key>
  3. 3

    Describe the tool

    Say what you need. Base44 builds it on top of the Powabase API. Try one of the examples below.

Example apps

Real apps, each from one prompt. Copy any of them and give it to Base44.

RAG support chatbot

Ingest our product docs, help center, and resolved tickets into a knowledge base, embedding on upload. Expose a support agent that answers with inline citations, streams over SSE, and hands off to a human when confidence is low. Add email and Google sign-in, isolate every conversation per organization with row-level security, and ship it as an embeddable chat widget.

Internal knowledge assistant

Index our wikis, runbooks, and exported threads into a knowledge base, chunking and embedding on upload. Expose an agent that answers with citations and respects per-department access, keep it fresh with scheduled re-indexing of changed sources, and add SSO sign-in plus an analytics view of unanswered questions.

AI help desk

Model tickets, organizations, and agents with row-level security, and auto-triage incoming tickets with an agent that predicts category and priority and drafts a reply from the knowledge base. Escalate low-confidence cases, run SLA timers as scheduled jobs, add email auth, and provide a live queue dashboard.

Sales CRM

Model companies, contacts, deals, and activities in Postgres with row-level security per team and roles for reps and managers. Build a pipeline board with stage tracking, an activity timeline, and semantic search across notes, plus a dashboard of weighted pipeline and win rate. Wire OAuth sign-in and an audit log of every change.

News monitoring app

Pull RSS feeds and news APIs on a schedule, deduplicate and embed each article, and run an agent that clusters related stories, summarizes them, and tags entities and sentiment. Let users define watchlists and alert rules, isolate data per workspace, and deliver a realtime feed plus a daily email digest via a cron job.

Invoice & receipt automation

Accept PDF and image uploads to storage, then extract vendor, line items, totals, and dates with an extraction agent and write validated records to Postgres, routing low-confidence fields to human review. Add approval workflows, per-team access control, exports to accounting formats, and a searchable archive.

Where Base44 keeps your keys

Base44 stores API keys as Secrets in the app dashboard and hands them only to backend functions, the TypeScript code under Dashboard → Code → Functions. Put BASE_URL and the Service Role key there and have a backend function make every Powabase call; the frontend Base44 builds should call that function, not Powabase. Backend functions need a Builder plan or higher. When you replace a key, preview picks it up right away, but the live app only uses it after you publish again.

Base44 docs

Connect over MCP

Add it from Settings → Account → MCP connections (GUI form).

GUI form
1. Click your workspace name at the bottom left, then Settings.
2. Under Account, click MCP connections, then Add custom MCP.
3. Name: Powabase
4. URL: https://mcp.powabase.ai/mcp
5. Authentication: OAuth
6. Click Test & add, then complete the Powabase sign-in.

MCP connections need a Builder plan or higher, and each account can hold up to 20. A connection works in the AI chat for every app your account can reach, but only while you build; your published app still calls Powabase from a backend function.

Append ?read_only=true to the MCP URL and the server exposes only the tools that don't write. We use it for sessions that should inspect a project and never mutate it.

Base44 MCP docs

Base44 example

Backend function (entry.ts)
import { createClientFromRequest } from "npm:@base44/sdk";
import { secrets } from "base44:runtime";

export default async function (req: Request): Promise<Response> {
  const user = await createClientFromRequest(req).auth.me();
  if (!user) return Response.json({ error: "Unauthorized" }, { status: 401 });

  const { message } = await req.json();
  const key = secrets.get("API_KEY")!; // Service Role (Secret) Key
  const url = `${secrets.get("BASE_URL")}/api/agents/${secrets.get("AGENT_ID")}/run`;
  const res = await fetch(url, {
    method: "POST",
    headers: { apikey: key, Authorization: `Bearer ${key}`, "Content-Type": "application/json" },
    body: JSON.stringify({ message }),
  });
  return new Response(await res.text(), {
    status: res.status,
    headers: { "Content-Type": "application/json" },
  });
}

Backend functions run on Deno. This one only answers signed-in users of your Base44 app, and it reads secrets inside the handler because they resolve per request.

Connecting to Powabase from any tool

Mechanics that don’t change from tool to tool.

Anon (Publishable) Key
Client-side
Respects Row Level Security, so it's safe to ship to a browser.
Service Role (Secret) Key
Server-side only
Bypasses RLS. Never put it in anything that ships to a browser.
Keys & RLS docs ↗
  • Every call to /api/* or /rest/v1/* needs two headers, apikey and Authorization: Bearer, both set to the same key. Sending only one is the most common cause of a 401.

    Docs
  • The Database URL from the Connect modal is PgBouncer in transaction mode, not a direct Postgres connection. Disable prepared statements in your driver, or you'll hit prepared statement "..." does not exist. No LISTEN/NOTIFY and no session-level SET across statements. Use Realtime for change notifications; SET LOCAL inside a transaction otherwise. The username and database in the URL are both your project ref, not postgres.

    Docs
  • @supabase/supabase-js mostly works for the BaaS surface (PostgREST, Auth, Storage, Realtime) when you point it at your project URL with the Anon key. It doesn't cover the /api/* AI surface (agents, knowledge bases, orchestrations), which you call over plain REST. There's no /graphql/v1 route: point any GraphQL client at POST /rest/v1/rpc/graphql instead.

    Docs

Common errors

Asking the AI chat for a Powabase integration doesn't produce a backend function
Cause: Backend functions need a Builder plan or higher.
Fix: Upgrade the plan, then ask again: name the Powabase endpoints you need and say the key should be stored as a Secret.
secrets.get("API_KEY") returns undefined
Cause: It's called at the top level of the module. Secrets resolve per request, so a read at module load happens before any are available.
Fix: Move the secrets.get calls inside the handler.
Preview works with your new key, but the published app still fails
Cause: A replaced secret applies to building and previewing straight away, but the published version keeps the old value.
Fix: Publish the app again.
401 Unauthorized
Cause: Only one of the apikey / Authorization headers was sent.
Fix: Send both, set to the same key. Docs
prepared statement "..." does not exist
Cause: PgBouncer's transaction-mode pooler moved you to a different server connection.
Fix: Disable prepared statements in your driver's config. Docs
A query that should return rows comes back empty, or a write is silently rejected
Cause: Row Level Security on your own tables. New public tables ship with RLS off, but once you add policies they gate every request.
Fix: Check the policy's USING/WITH CHECK clause and confirm which role (anon, authenticated, service_role) you actually authenticated as. Docs
The Service Role key turns up in a browser bundle or other client-visible code
Cause: It was used somewhere that ships to the client instead of staying server-side.
Fix: Move the call server-side; use the Anon key with RLS for anything client-visible. If it shipped, rotate it in Studio. Docs

FAQ

Yes, through a backend function and Secrets. Powabase isn't one of Base44's built-in integrations or connectors, so you describe the integration in the AI chat, give it the Service Role key as a Secret, and Base44 writes the function that calls the Powabase API.

Yes. Backend functions, which is where external API calls with your own keys run, need a Builder plan or higher. Custom MCP connections have the same requirement.

In the app's Secrets, as API_KEY alongside BASE_URL. Backend functions read them with secrets.get(); they never reach the frontend code Base44 generates.

Yes, on Builder and above. Add https://mcp.powabase.ai/mcp under Settings → Account → MCP connections with OAuth. The chat calls it when your prompt needs Powabase data, for example to read your table structure before it builds a screen.